Theo Hughes · 8 October 2026
How Specialized Platforms Like Cadouna Reshape Compliance Workflows in Heavily Regulated SaaS Sectors
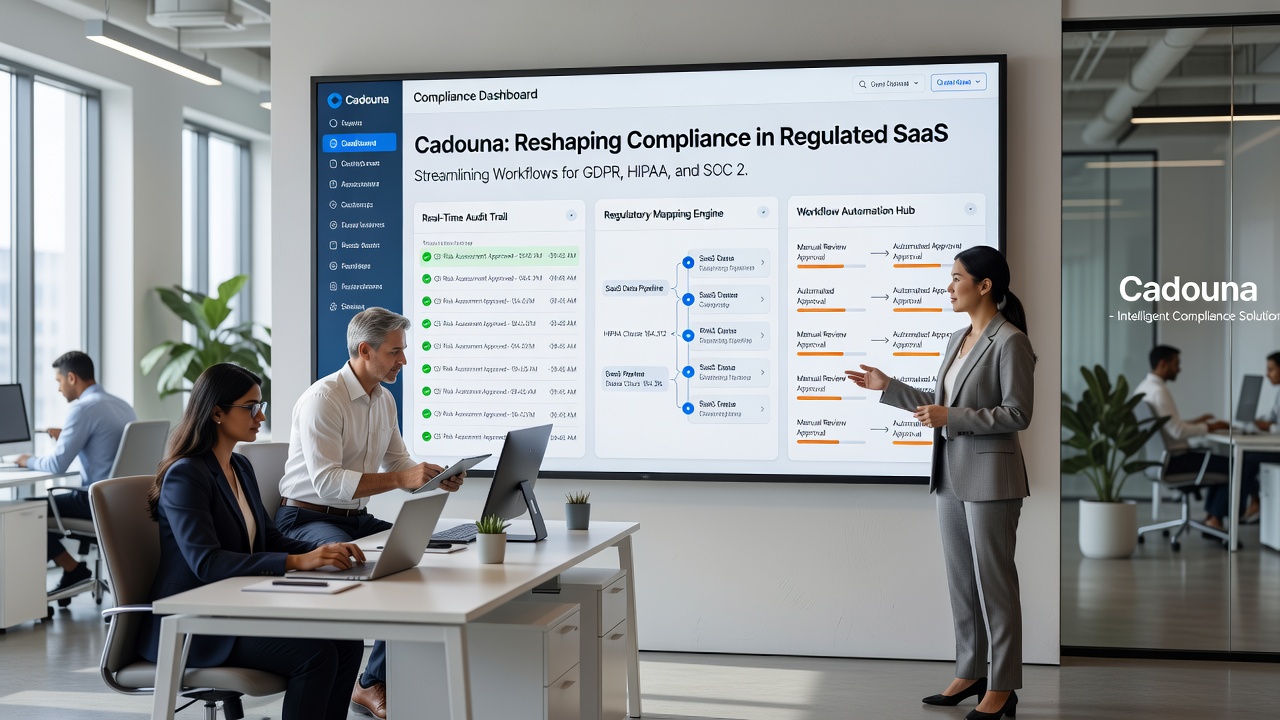
Specialized platforms such as Cadouna integrate directly into SaaS environments where regulations like HIPAA, GDPR, and SOC 2 create continuous documentation and monitoring requirements, and teams often handle overlapping obligations across multiple jurisdictions at once. These systems connect with existing code repositories, cloud providers, and identity management tools so that policy enforcement happens during development rather than after deployment, while audit trails generate automatically from each interaction.
Core Mechanisms Driving Workflow Changes
Researchers tracking SaaS operations note that platforms like Cadouna replace manual spreadsheet tracking with automated mapping of controls to specific regulatory clauses, and the process begins when code commits trigger scans that flag deviations against predefined rule sets. Data from deployment logs flows into centralized repositories where version history remains tied to each compliance decision, allowing teams to reconstruct events without recreating records from separate sources. In October 2026 updates to data residency rules across several regions, such platforms adjusted mapping rules in real time so organizations maintained alignment without pausing release cycles.
Integration Patterns Observed in Regulated Environments
Those who study enterprise SaaS deployments report that Cadouna-style tools embed within CI/CD pipelines so that security and privacy checks execute alongside functional tests, and results appear in shared dashboards accessible to engineering, legal, and operations groups. Configuration drift detection runs continuously against baseline policies derived from frameworks published by the National Institute of Standards and Technology, while alerts route to responsible owners through existing ticketing systems rather than creating parallel processes. One study of distributed teams revealed that organizations using these platforms reduced the time spent preparing for external audits by consolidating evidence collection into a single query interface that pulls from multiple cloud accounts simultaneously.
Integration extends to third-party vendor assessments as well, where questionnaires receive pre-populated answers drawn from live system data instead of static documents updated quarterly. External links pull regulatory text directly so that any amendment appears in the platform's rule engine within days of publication, keeping internal policies synchronized without manual intervention.
Sector-Specific Adaptations
In healthcare SaaS products handling protected health information, observers have documented how Cadouna instances enforce encryption standards and access logging at the object level while maintaining HIPAA audit requirements across multi-tenant architectures. Financial technology providers see similar patterns where transaction monitoring rules align with both domestic reporting mandates and cross-border data transfer restrictions, and the platform maintains separate rule sets that activate based on user location and data classification tags. Research indicates that organizations in these sectors achieve consistent policy application across development, staging, and production environments because the same control definitions apply throughout the lifecycle rather than requiring translation between teams.
Academic analyses of compliance automation highlight reduced duplication when evidence for one regulation satisfies overlapping requirements in another, and platforms surface these overlaps through visual dependency graphs. Teams then allocate review time to genuinely distinct obligations instead of repeating the same verification steps across frameworks.
Measurement and Reporting Shifts
Figures from industry reports show that automated platforms shorten the interval between identifying a control gap and generating remediation tickets, because detection logic connects directly to workflow tools already in use. Continuous compliance dashboards replace periodic snapshots, giving stakeholders visibility into current status rather than historical points in time. The Australian Office of the Information Commissioner guidance on privacy management plans aligns with this approach, as platforms can export formatted reports matching regulatory templates without additional formatting steps.
Those monitoring SaaS maturity note that the shift also changes staffing models, with fewer personnel dedicated exclusively to evidence gathering and more focused on interpreting results or refining control logic. Training shifts accordingly toward platform configuration and rule maintenance rather than document assembly techniques.
Conclusion
Platforms built around specialized compliance automation continue to alter how regulated SaaS organizations structure daily operations, audit preparation, and cross-team coordination. By embedding checks into existing development and deployment processes while maintaining connections to regulatory sources, these systems create traceable records that support multiple frameworks without requiring repeated manual effort. As regulatory landscapes evolve, the same architecture allows incremental rule updates rather than wholesale process redesigns.